Quality Management System
Watanabe Electric Industry acquired the ISO9001:2008 Certification, for the purpose of “achieving further customer satisfaction” and improving the quality of the company. Since the company was founded in 1940, we have continued to promote development, manufacturing and sales of measurement and control instruments, and have received consistent evaluations from society. However, only the enthusiasm and actions of each employee is not enough to achieve “continued manufacturing of products which will provide maximum customer satisfaction, and continue to create a company which uses customer satisfaction as the roots of our growth” which is our corporate philosophy.
We established a Quality Management System as required by ISO, created documentation and constructed a “Target Achievement System” for our company, in order to implement and maintain a Quality Management System, and by utilizing this system, we can certainly achieve the corporate philosophy of our company. Particularly, in regards to “quality”, “delivery” and “costs” which are the most important items for a manufacturer, we created a system of standards, manuals and procedures suitable to the actual conditions of our business, which can be used as an “effective tool in the standardization of operations”.
The created systems will be practiced in the business operations as a management tool, to continuously revise and improve the compatibility and effectiveness even further. We will improve the quality of Watanabe Electric Industry Co. Ltd., so that more customers will continue to do business with our company.
Quality Policy – Achieving Objective Quality –
The target of our company is to realize the corporate philosophy and management policy, and by achieving the objective quality which will lead to the utmost satisfaction of customers, the brand image “Watanabe Electric Industry Co. Ltd. is reliable” will be established.
Information Security Management System
To further strengthen information security and become a company that earns even greater trust from our customers, our Hardware Development and Software Development Divisions have obtained ISO 27001 certification (Information Security Management System). To achieve certification, we established an information security management system and implemented it throughout the company, leading to successful certification. Through this system, we ensure the confidentiality, integrity, and availability of information handled in our business activities for the appropriate management and protection of information assets, and continuously work to improve information security.
Basic Information Security Policy
We protect information entrusted to us by our customers, as well as important information assets used in our business, from threats such as loss, alteration, leakage, and unauthorized use. To meet the trust of our customers and society, we maintain and improve information security based on the following policy.
Code of Conduct
1.Organization
We appoint an executive responsible for overseeing the Information Security Management System and promote appropriate information security measures and activities.
2.Compliance with Laws and Regulations
We comply with laws, regulations, and standards related to information security. We also ensure that we fulfill our contractual obligations and strive to build trusting relationships with our business partners.
3.Information Asset Management
We implement appropriate organizational and technical measures to ensure the confidentiality, integrity, and availability of information assets, and respond to evolving information technologies and emerging threats.
4.Employee Training
We provide information security training to all employees, ensure thorough communication of this policy, and work to enhance and maintain their awareness.
5.Review and Improvement
We establish objectives for the management system and information security, review them regularly, and continuously improve and maintain them.
Established on December 1, 2025.
Watanabe Electric Industry Co. Ltd.
President Yohei Harada
Product Security
Security Lifecycle Policy
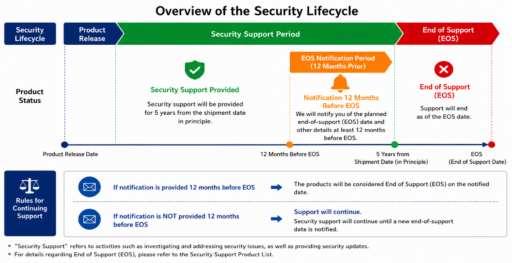
Our company has established a Security Lifecycle Policy to provide after-sales services, including product security support, for as long as reasonably practicable.
In principle, for separately designated products, we provide security support for five years from the product’s release and continue to provide support beyond five years unless an End of Service (EOS) notice is issued.
EOS is declared when continued support becomes difficult, for example due to the end of support for third-party components, and in principle we announce EOS at least one year in advance.
This policy defines how we handle high-severity vulnerabilities and the level of support after an EOS notice, and it advises customers to apply appropriate updates and migrate to successor products.
Vulnerability Management
We have established the Watanabe Electric PSIRT (WE-PSIRT) as our product security response organization.
WE-PSIRT collects vulnerability information related to our products and makes every effort to take prompt and appropriate measures.
Vulnerability Disclosure Policy
The Company accepts vulnerability reports from external parties and responds promptly to improve the security of our products and services. This policy provides guidelines for reporting vulnerabilities regarding our products and establishes a framework for the reporter and the Company to cooperate in improving security. Through this, we aim to ensure the safety of our customers and society as a whole and provide highly reliable products and services.
Product Vulnerability Reporting Desk
Information on Vulnerabilities
Employee Certifications
To deliver even greater trust and reassurance to our customers, we never neglect self-improvement. We face each day with a continuing spirit of growth and ambition.
List of Acquired Certifications
National Certifications Related to Energy
Energy Manager Certification
National Certifications Related to Information Technology
Embedded Systems Specialist
Systems Architect
Applied infomation technology engineer
Fundamental information technology engineer
IT passport
Electric Engineering national qualifications
Class 3 chief electrical engineer
2nd calss electrical construction management engineer
2nd calss licensed electrical engineer
National qualifications for building construction in japan
1st class architect
1st class Civil Engineering Works Execution Managing Engineer